I recently came across an older ColdFusion 2018, update 12, server that was many patches behind. I can't go into details on this server's origin.
We noticed that one of many websites on this single Windows IIS server returned a "Failed to add HTML header" a couple of times. This site still uses FuseBox 3.1. Then the site just started returning empty content, with no error and a valid 200 HTTP code. No errors logged in the ColdFusion logs.
We noticed a .jpg file in the root with a recently modified date that did not belong there, and the robots.txt was recently updated.
The .jpg file contained malicious PHP code, while the robots.txt file had the following appended:
# Sitemap: http://{url}/?sitemap=1&type=index# AUTH:upload/7FD4B026F124.jpg
I am not positive why it added a sitemap reference.
If you deleted the .jpg file, it recreated it and appended another "AUTH:" line when the site was hit again, due to a cfinclude (in this case it was in the index.cfm).
When looking at FusionReactor, we saw HTTP calls being made to api.cdnapi.tech. Unknown the reason for those, but it's malicious. Check your code for this.
We also found suspicious requests for cf_script/clients.cfm in the IIS logs. That name mimics ColdFusion's client-variables handler, and the file did not belong on the server. I am not publishing that code.
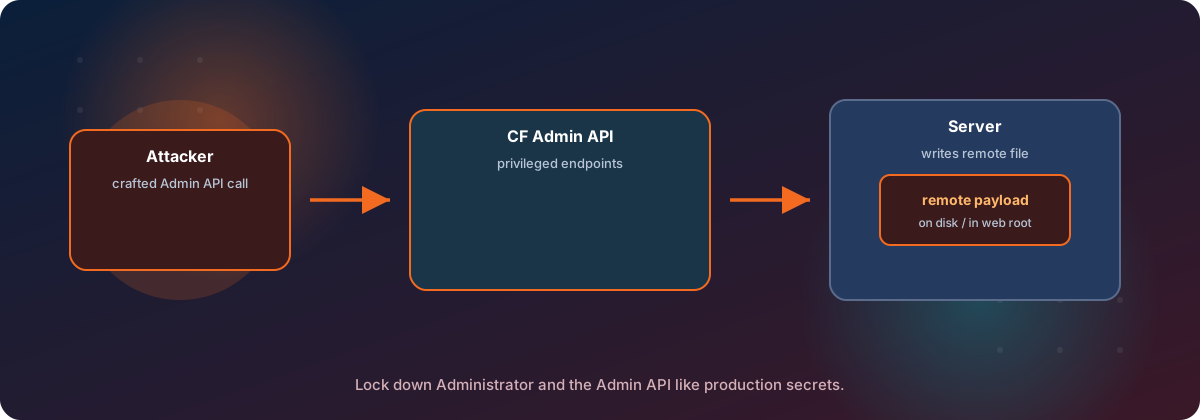
Log review showed the administrator API had been reached through a directory-traversal bypass, CVE-2023-29298. Search IIS logs for .. in paths that point at CFIDE/adminapi. Requests to the admin API that did not use directory traversal were unsuccessful. A follow-up on the original post also ties similar scanning to CVE-2024-20767 in the Performance Monitoring Toolset.
These requests were scattered over a period of about a month.
As an immediate step, block requests whose URI contains .. in the web application firewall. Blocking a single folder prefix is not enough, because the traversal is not tied to one name. This server still needed the ColdFusion updates that close the issue.
This information is to help other ColdFusion admins narrow down a similar compromised server as a reference. This particular server is getting the needed updates and resolution.
If you need assistance with a compromised server, reach out to me or Tierney Dynamics to help you in a time of crisis.
Comments